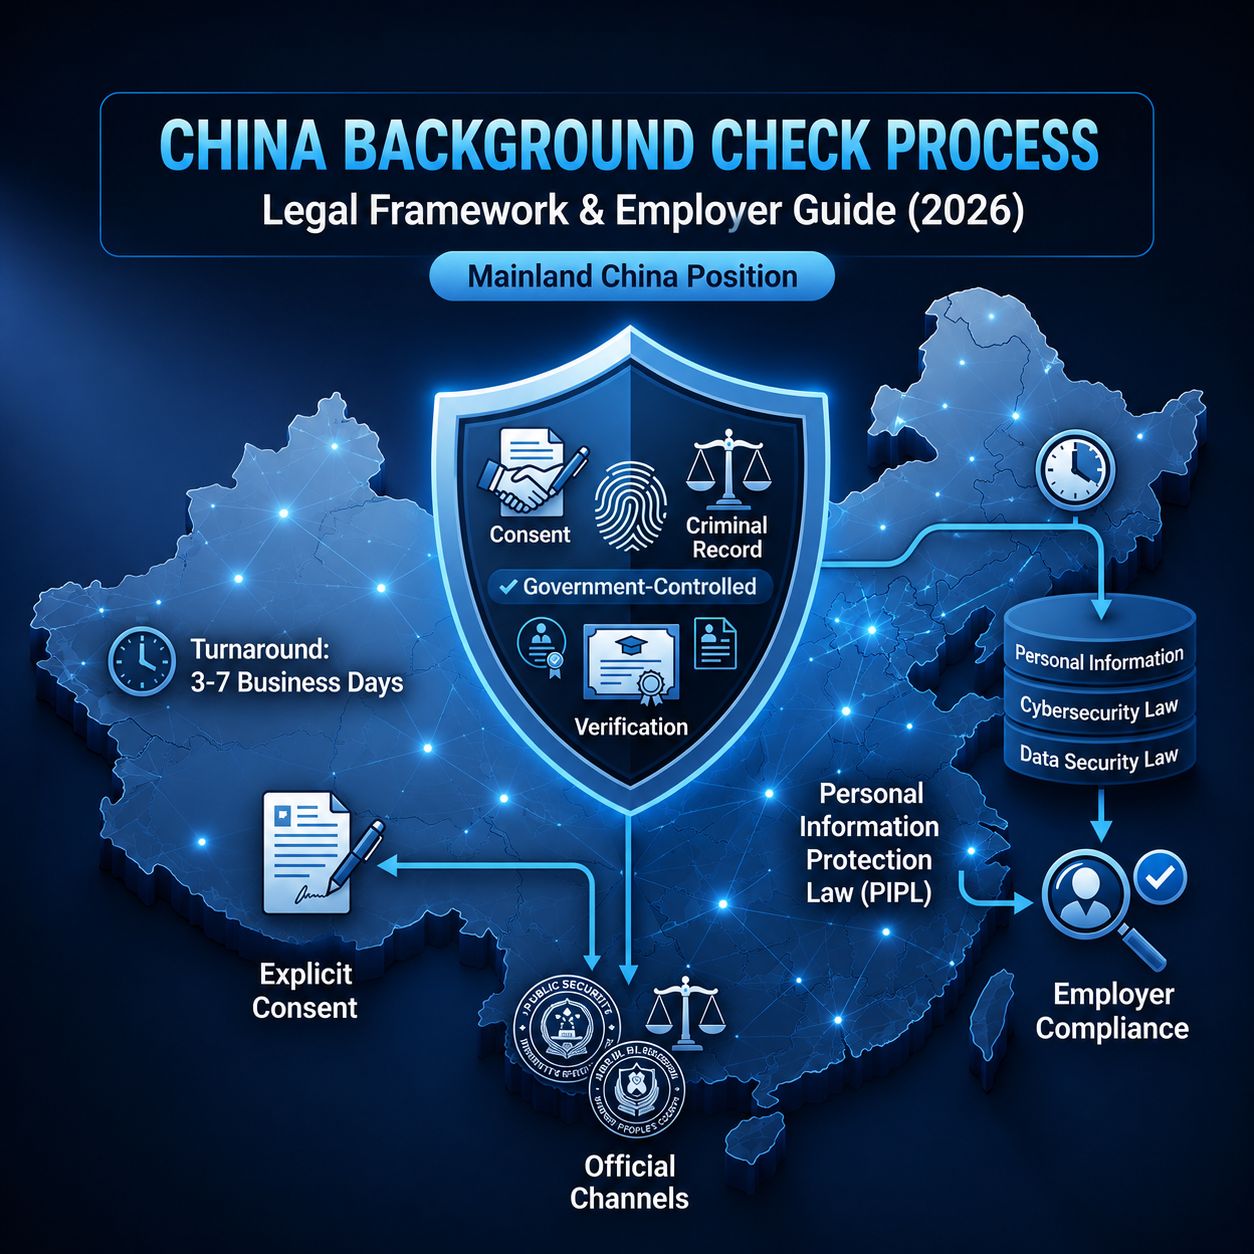
China Background Check Process: Legal Framework & Employer Guide (2026)
A comprehensive overview of employment screening in Mainland China.Published: May 12, 2026 | Last Updated: September 11, 2026
Executive Summary
Background screening in Mainland China operates within a complex regulatory environment shaped by data protection, cybersecurity, and localization requirements. Employers must ensure strict compliance with consent, criminal record access controls, and cross-border data rules. Download PDF Guide For broader Asia compliance frameworks, see: Compliant Background Screening Policy AsiaChina Background Check – At a Glance
| Category | Mainland China Position |
|---|---|
| Legal Framework | PIPL, Cybersecurity Law, Data Security Law, Network Data Security Management Regulations |
| Consent | Legal basis required; consent rules depend on the processing activity |
| Criminal Record Access | Government-controlled certificate |
| Employment Verification | Institution-dependent |
| Education Verification | Common but fraud risk exists |
| Credit Check | Restricted |
| Data Localization | Highly relevant |
| Cross-Border Transfer | Regulated; exemption, Standard Contract / certification, or CAC security assessment may apply |
| Operational Complexity | High |
| Turnaround | 3–7 business days depending on check type |
1. Legal Framework in China
Screening is governed by:- Personal Information Protection Law (PIPL)
- Cybersecurity Law
- Data Security Law
- Network Data Security Management Regulations
Official legal sources: Personal Information Protection Law of the PRC and Network Data Security Management Regulations.
For wider compliance planning, see:
Asia Compliance Guide
2. Consent Requirements
PIPL does not make written consent the only possible legal basis for every background-screening activity. Employers should first identify the applicable legal basis for each processing activity. Where processing relies on consent, the consent must be voluntary, explicit, and based on full knowledge of the purpose, method, and scope of processing. For background screening, employers should clearly document:- The purpose and scope of the screening
- The categories of personal information involved
- How the information will be used and retained
- Any third-party processors involved
- Whether personal information will be transferred outside Mainland China
- Whether separate consent or additional notice is required for a particular processing activity
PIPL point: Article 13 provides several legal bases for processing personal information, including consent and, in specified circumstances, processing necessary for human-resources management under legally formulated labour rules and legally concluded collective contracts. Where consent is the basis, Article 14 requires voluntary and explicit consent given on a fully informed basis.
See our template:
Background Screening Policy Template
3. Criminal Record Checks
Criminal record access in Mainland China is tightly controlled. Criminal record certificates must generally be requested by the individual and issued by the local Public Security Bureau.| Requirement | Details |
|---|---|
| Access | Strictly controlled |
| Application | Candidate must apply |
| Authority | Public Security Bureau (PSB) |
| Employer Use | Must be role-relevant and legally justified |
- Confirm whether the role justifies a criminal record check.
- Obtain explicit candidate consent.
- Use official government-issued certificate routes only.
- Avoid unofficial criminal databases.
- Document the decision-making basis.
4. Employment Verification in China
Employment verification in China can be more complex than in some jurisdictions. Challenges include:- Company responsiveness variability
- Regional differences in record retention
- Corporate restructuring history
- Limited standardized HR documentation
- HR department confirmation
- Supervisor confirmation
- Supporting employment proof documents
5. Education Verification & Fraud Risk
Education fraud risk in China is higher compared to some other Asian markets. Education verification typically includes:- Degree authenticity confirmation
- Institution accreditation validation
- Cross-check against official registries where applicable
- Document validation
- Direct institutional contact
- Database cross-referencing
- Senior hires
- Technical roles
- Executive positions
6. Credit & Financial Checks
Credit reporting in China is regulated. Access to individual credit data is restricted, requires explicit consent, and may be limited in scope. Credit checks are restricted and require:- Explicit consent
- Role-based justification
- Legal permissibility review
- Sensitive data handling controls
- Clear retention limits
7. Litigation & Risk Checks
Additional risk screening may include civil litigation searches, adverse financial records, and legal representative searches. These checks provide broader visibility into legal and financial risk exposure.| Check Type | Purpose |
|---|---|
| Civil Litigation | Identifies court cases, legal disputes, and potential civil exposure |
| Dishonesty List (失信人) | Identifies enforcement actions and court-ordered obligations |
| Legal Representative Search | Identifies company legal representative roles, corporate involvement, and potential exposure |
- Use only where relevant to the role.
- Assess proportionality before collection.
- Document the reason for conducting the check.
- Review findings carefully before making employment decisions.
8. Cross-Border Data Transfer for China Background Screening
China regulates the transfer of personal information and important data outside Mainland China. For multinational hiring, this may apply when candidate or employee screening information is accessed by an overseas headquarters, regional HR team, affiliate, or screening provider. The applicable route depends on the type of data, whether sensitive personal information or important data is involved, whether the organisation is a critical information infrastructure operator (CIIO), the annual volume of exported data, and whether an exemption applies.8.1 Current Cross-Border Transfer Thresholds
| Scenario | General Position |
|---|---|
| Non-CIIO exporting fewer than 100,000 individuals’ non-sensitive personal information | May qualify for exemption from the CAC security assessment, Standard Contract, and certification mechanisms, subject to the March 2024 rules. |
| Non-CIIO exporting 100,000 to fewer than 1 million individuals’ non-sensitive personal information | Standard Contract or certification generally applies, unless an exemption applies. |
| Non-CIIO exporting fewer than 10,000 individuals’ sensitive personal information | Standard Contract or certification generally applies, unless an exemption applies. |
| Non-CIIO exporting 1 million or more individuals’ non-sensitive personal information, or 10,000 or more individuals’ sensitive personal information | CAC security assessment is generally required. |
| Important data, or PI / important data exported by a CIIO | CAC security assessment is required. |
Primary source: These thresholds are based on the CAC Provisions on Facilitating and Regulating Cross-Border Data Flows, issued 22 March 2024.
8.2 HR Management and Recruitment Considerations
The March 2024 Provisions include an exemption from the three data-export mechanisms where it is genuinely necessary to transfer employee personal information overseas for cross-border HR management under legally formulated labour rules and legally concluded collective contracts. This is not a blanket exemption for all HR or recruitment data. Employers should still assess the specific purpose, data scope, recipients, and other PIPL obligations. CAC’s July 2026 guidance also states that where an overseas headquarters or affiliate does not participate in the Mainland China hiring decision, transferring applicant information overseas may lack necessity. Where the overseas entity does participate, the number of applicants and the data fields transferred should be limited to what is necessary. Where separate consent is legally required for an overseas transfer, it should be specific rather than bundled into blanket authorisation.2026 CAC guidance: See CAC Data Export Security Management Policy and Regulation Q&A (July 2026).
8.3 Practical Employer Checklist
- Identify exactly what candidate or employee data will leave Mainland China.
- Determine whether sensitive personal information or important data is involved.
- Confirm whether the organisation is a CIIO.
- Calculate the relevant annual export volume.
- Check whether a statutory exemption applies.
- If no exemption applies, determine whether Standard Contract, certification, or CAC security assessment is required.
- Assess notice, consent, and personal information protection impact assessment requirements.
9. Risk Sensitivity Matrix
Criminal, credit, litigation, financial risk, and cross-border data transfer checks require careful compliance management.| Check Type | Sensitivity Level | Legal Review Recommended |
|---|---|---|
| Identity | Moderate | No |
| Employment | Moderate | No |
| Education | Moderate | No |
| Criminal | High | Yes |
| Credit | High | Yes |
| Litigation and Financial Risk | Moderate–High | Yes |
| Social Media | High | Yes |
| Regulatory History | Moderate–High | Yes |
| Cross-Border Transfer | High | Yes |
10. Typical Turnaround Time
Turnaround depends on the type of check, local government processes, institutional responsiveness, geographic region, document quality, and candidate cooperation.| Check Type | Estimated Time |
|---|---|
| Identity | 1–3 business days |
| Employment | 3–7 business days |
| Education | 1–3 business days |
| Criminal | 3–7 business days |
| Credit | 3–7 business days |
| Litigation & Financial Risk | 1–3 business days |
| Regulatory / Sanctions | 1–3 business days |
- Local government processes
- Institutional responsiveness
- Geographic region
- Document quality
- Candidate cooperation
11. Common Mistakes
China requires jurisdiction-aware precision. Employers should avoid assuming that screening practices from other markets can be applied without localization.| Mistake | Risk |
|---|---|
| Ignoring cross-border rules | Regulatory penalties |
| Using unofficial data | Legal violation |
| Over-collecting data | PIPL breach |
| Wrong consent format | Non-compliance |
| Assuming national uniformity | Operational failure |
12. Executive Oversight Checklist
Senior management should ensure China background screening is properly governed, documented, and aligned with legal requirements.| Governance Question | Yes / No |
|---|---|
| Is consent compliant with PIPL? | |
| Is criminal verification obtained through official channels? | |
| Are cross-border transfers assessed? | |
| Is sensitive data classified properly? | |
| Is screening scope role-proportionate? | |
| Is documentation retained securely in China? |
Internal Resources
Risk-Based Screening
Asia Background Check Guide
Executive Briefing
Vendor Questions
In-house vs Outsourced
Top Firms Asia
HK Background Check Guide
Common Mistakes
Singapore Guide
HK Criminal Record Guide
FAQ
Is background screening legal in Mainland China?
Yes, provided it complies with PIPL and data protection laws.
Can data be transferred outside China?
Yes, but subject to strict cross-border data transfer regulations.
Is education fraud common?
Yes, verification is strongly recommended for key roles.
Is China screening complex?
Yes, due to regional variation and strict data regulations.
Does PIPL always require consent for a China background check?
No. PIPL Article 13 provides several legal bases for processing personal information. Consent is one basis, while specified human-resources management activities may rely on another legal basis where the statutory conditions are met. The appropriate basis should be assessed for the specific screening activity.
Can employee background-screening data be transferred outside Mainland China?
Potentially yes, but the organisation must assess the applicable PIPL and data-export requirements, including the type and volume of information, whether sensitive personal information or important data is involved, whether an exemption applies, and whether a Standard Contract, certification, or CAC security assessment is required.
When is a CAC security assessment required for personal information exports?
Under the March 2024 Provisions, a non-CIIO generally requires a CAC security assessment when exporting 1 million or more individuals’ non-sensitive personal information or 10,000 or more individuals’ sensitive personal information from 1 January of the current year, subject to applicable exemptions. CIIOs and exports of important data are subject to separate security-assessment requirements.
Is there an exemption for cross-border HR management?
Yes. The March 2024 Provisions provide an exemption from the three data-export mechanisms where it is genuinely necessary to provide employee personal information overseas for cross-border HR management under legally formulated labour rules and legally concluded collective contracts. It should not be treated as a blanket exemption for all HR data.
Can China candidate information be sent to an overseas headquarters for a hiring decision?
CAC’s July 2026 guidance says necessity should be assessed carefully. If the overseas headquarters or affiliate does not participate in the Mainland China hiring decision, the transfer may lack necessity. Where it directly participates, the number of applicants and data fields transferred should be limited to what is necessary and the applicable data-export requirements should be followed.
Is separate consent required when personal information is transferred overseas?
Where separate consent is legally required, CAC’s July 2026 guidance says it should be specific and not bundled into blanket authorisation. Where another applicable legal basis under PIPL Article 13 applies, consent may not be required, although cross-border notice obligations can still apply.

